Analytics
&
Security
We transform data chaos into clear strategic decisions.Your security is our priority.
Development and implementation of a comprehensive turnkey HR security policy to protect against internal threats.
Development and implementation of a comprehensive turnkey HR security policy to protect against internal threats.
Deep background check of applicants for key positions within 24–72 hours.
Professional lie detector testing to uncover hidden motives and facts of theft.
Fast and absolutely confidential conduct of internal corporate investigations.
Detailed analysis of legal entities and counterparties before signing contracts, deals, or partnerships.
Detailed analysis of legal entities and counterparties before signing contracts, deals, or partnerships.
Comprehensive assessment of the reliability of potential partners, counterparties, and business projects.
Legal analysis and identification of property assets of individuals and legal entities in Ukraine and foreign jurisdictions.
Monitoring and analysis of counterparty credit history, financial discipline, and debt burden.
Building reliable network protection, configuring firewalls, and intrusion detection systems (IDS/IPS).
Building reliable network protection, configuring firewalls, and intrusion detection systems (IDS/IPS).
Implementing DLP systems and controlling access to confidential corporate information.
Protecting servers and employee computers from ransomware and spyware.
Prompt assistance during breaches: containing the attack, investigating causes, and restoring systems.
Implementation and audit of privileged access management systems to control admin accounts and protect critical assets.
Implementation and audit of privileged access management systems to control admin accounts and protect critical assets.
Comprehensive review of IT systems for vulnerabilities and misconfigurations in security settings.
Finding loopholes in source code that could lead to unauthorized access.
Professional cybersecurity project management and PoC execution to verify solution effectiveness.
Analysis of competitors and market trends for strategic decision-making.
Analysis of competitors and market trends for strategic decision-making.
Legal data collection on strategies and plans of your competitors based on open sources.
Deep intelligence reports combining digital footprints and registry data for a complete picture.
24/7 monitoring of brand reputation and detection of informational attacks in the media.
Confidential gathering and analysis of information, fact-checking, and resolving sensitive issues.
Confidential gathering and analysis of information, fact-checking, and resolving sensitive issues.
Comprehensive protection of business owners and top managers from internal and external threats.
Professional consultations on building a complete business security architecture from scratch.
Staff training on countering social engineering, phishing, and safe data handling.
Uncovering hidden assets and connections in a complex corporate network.
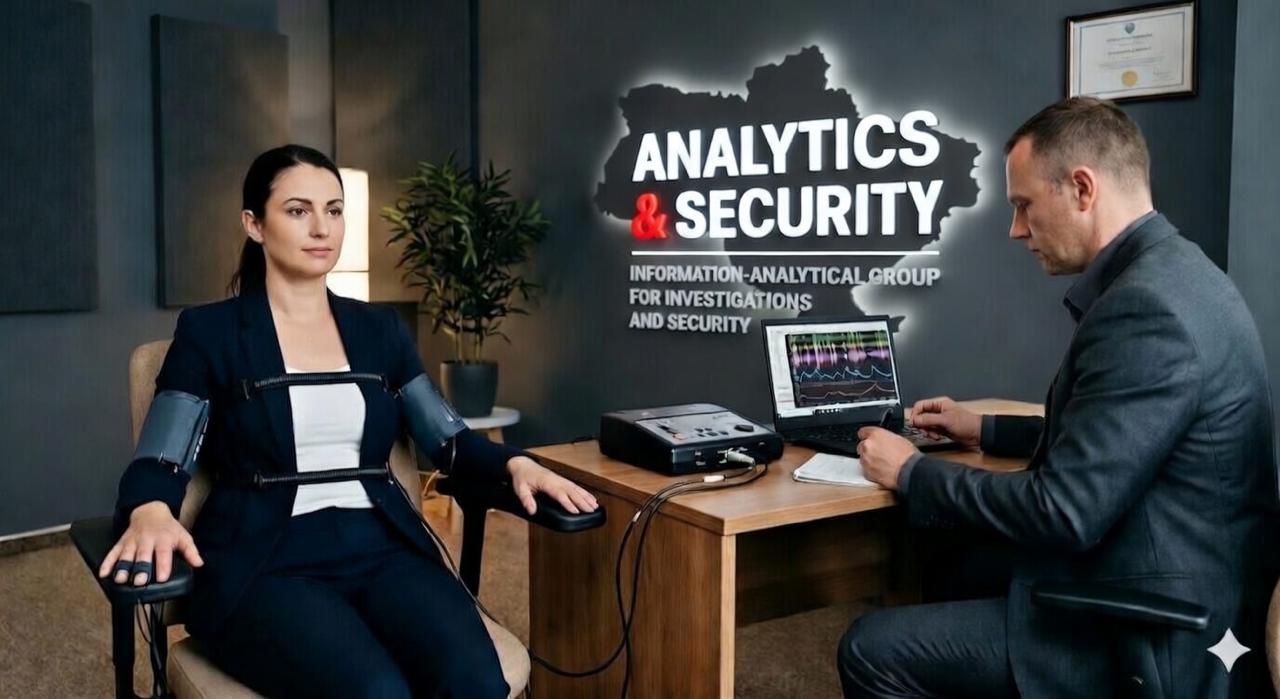
How a polygraph protects an honest name and finds the guilty in delicate family situations.
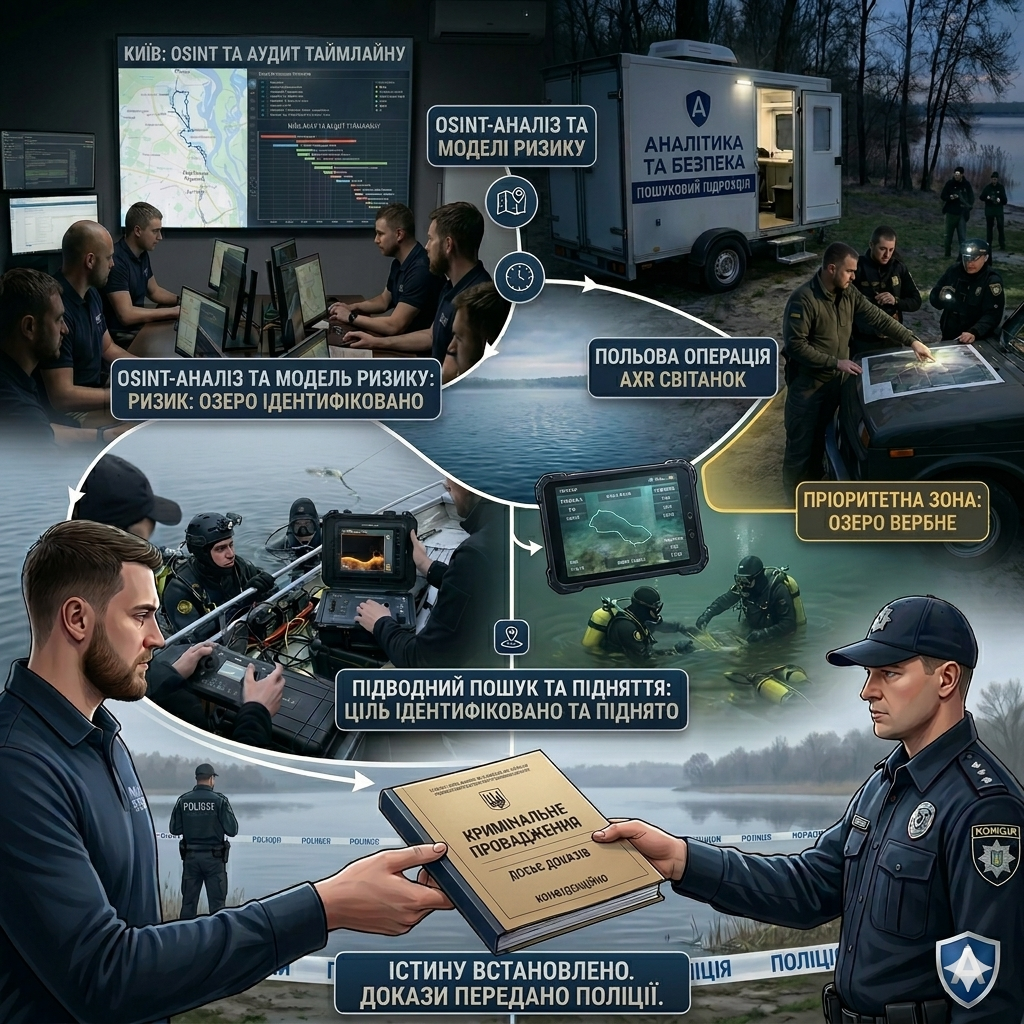
Emergency search for a missing person using OSINT analytical methods and coordinated search team efforts.
Countering confidential data leaks and setting up security.
Problem: The client suspected top management of siphoning assets through shell companies, but had no direct evidence. The scheme was disguised through a network of offshores and nominee owners.
Actions: The Analytics & Security team conducted a deep OSINT analysis, tracing digital footprints and connections between key figures. We analyzed registries, social networks, and document metadata.
Result: A hidden network through which funds were withdrawn was uncovered. The report allowed the client to successfully recover the assets.
The owner of a private house contacted us. A large sum of money had disappeared from the safe. Everyone was under suspicion: the wife, the nanny, and the security guard who had been working there for 5 years.
Problem: The atmosphere in the family became unbearable. The owner did not want to go to the police without evidence to avoid ruining the reputation of innocent people, but leaving the crime unpunished was also impossible.
Investigation process: Our expert polygraph examiner developed a testing methodology using the «concealed information» technique (details known only to the perpetrator).
- Wife and nanny: No physiological reactions. Complete non-involvement.
- Security guard: During questions about the method of entry, the sensors recorded sharp changes in blood pressure and skin resistance. Attempts to manipulate breathing were detected.
Result: After 1.5 hours of testing, the security guard confessed to the crime due to gambling debts. The money was returned, the innocent were cleared of suspicion, and peace in the family was restored.
Problem: Analytics & Security was contacted by the relatives of a young man who suddenly disappeared at night in Kyiv. The only piece of physical evidence at the initial stage was the missing person's mobile phone, found by passersby.
Analytics & OSINT: Specialists conducted a digital footprint audit, reconstructed the timeline of his movements from Poshtova Square, and verified eyewitness testimonies.
Localization: Based on geospatial data analysis, we built a risk model and identified the local lake area as the priority search zone. A mobile headquarters was established to coordinate teams.
Technical Stage: Due to the high probability of the object being in the water, we engaged a professional dive team with specialized equipment to survey the silted bottom in zero-visibility conditions.
Result: Thanks to precise sector analysis, the missing person was located. All materials were transferred to law enforcement. Our team performed a comprehensive scope of work, helping the family uncover the truth in this tragic event.
Problem: Our client noticed that their technical documentation ended up with competitors. Internal attempts to find the source yielded no results, and the risk of reputational loss was growing.
Actions: We conducted an information security audit and a "digital manhunt". Using social engineering and technical analysis methods, we identified an employee trading data on the DarkNet.
Result: We helped the client safely terminate the relationship with this employee and closed the vulnerability. We also configured a monitoring system (DLP) to prevent such incidents from happening in the future. The client's business is now under reliable protection.